What Is VAPT in Cybersecurity? Meaning, Types, Benefits and Tools
Summarize this blog with :
Vulnerability Assessment and Penetration Testing (VAPT) is a critical part of modern cybersecurity, helping organisations identify security weaknesses before attackers can exploit them. This guide explains what VAPT means, its types, benefits, testing process, commonly used tools, and how VAPT services help strengthen security, manage risks, and protect digital assets.
The Basics of VAPT
What Is VAPT?
VAPT stands for Vulnerability Assessment and Penetration Testing. It is a cybersecurity testing approach that helps organisations identify, evaluate, and address security weaknesses across their IT infrastructure, networks, applications, and systems.
VAPT combines two complementary security practices: Vulnerability Assessment and Penetration Testing. While Vulnerability Assessment identifies potential security gaps, evaluates their severity, and recommends remediation measures, Penetration Testing simulates real-world cyberattacks to determine whether these vulnerabilities can actually be exploited.
Together, these processes provide a comprehensive view of an organisation's security posture, helping security teams prioritise risks, strengthen existing defences, and reduce exposure to cyber threats.
Method
Description
Vulnerability Assessment
Identifies security weaknesses, assigns severity ratings, and recommends corrective measures.
Penetration Testing
Simulates controlled cyberattacks to determine whether identified vulnerabilities can be exploited.
Combined VAPT
Provides a comprehensive security assessment and supports proactive vulnerability remediation.
Difference Between Vulnerability Assessment and Penetration Testing
Although both practices aim to strengthen cybersecurity, Vulnerability Assessment and Penetration Testing serve different purposes.
Vulnerability Assessment: focuses on identifying and evaluating security weaknesses across systems, networks, and applications. It uses automated scanning and manual analysis to discover vulnerabilities, classify them according to severity, and recommend appropriate remediation measures.
Penetration Testing: On the other hand, it goes a step further by simulating controlled attacks against identified systems. With the organisation's authorisation, security professionals attempt to exploit vulnerabilities to understand their potential impact and evaluate the effectiveness of existing security controls.
The key difference is that Vulnerability Assessment identifies and prioritises security weaknesses, whereas Penetration Testing validates their exploitability and potential consequences.
Key Objectives of VAPT in Cybersecurity
The primary objective of VAPT in cybersecurity is to help organisations identify and address security weaknesses before malicious attackers can exploit them.
Its key objectives include:
Identify security vulnerabilities: Discover weaknesses across internal and external networks, applications, servers, and IT assets.
Evaluate new systems and applications: Assess security before deploying new products, software versions, or infrastructure at scale.
Support regulatory compliance: Help organisations address security requirements under applicable regulations and standards.
Protect critical business assets: Safeguard sensitive information, intellectual property, financial records, and customer data.
Strengthen IT infrastructure: Improve security controls through proactive identification, assessment, and remediation of vulnerabilities.
The Importance and Benefits of VAPT
Why Do Organisations Need VAPT?
As organisations increasingly depend on digital infrastructure, applications, cloud platforms, and interconnected networks, their exposure to cyber threats continues to grow.
Regular VAPT testing helps businesses identify security weaknesses before attackers can take advantage of them. It provides valuable insights into potential attack paths, evaluates the effectiveness of existing security controls, and helps organisations make informed decisions about cybersecurity investments.
VAPT also supports compliance efforts by helping organisations assess their security practices against applicable requirements and standards, including GDPR, ISO/IEC 27001, and PCI DSS.
By proactively identifying and addressing vulnerabilities, organisations can reduce the likelihood of security incidents, protect critical business information, and maintain customer and stakeholder trust.
Five Major Types of VAPT
VAPT services cover different technology environments, depending on an organisation's infrastructure, applications, and security requirements.
The five commonly performed types of VAPT include:
1. Network VAPT
Network VAPT evaluates the security of an organisation's internal and external network infrastructure. It identifies vulnerabilities such as open ports, insecure configurations, outdated services, and weaknesses in network security controls.
2. Web Application and API VAPT
Web application and API VAPT identifies security weaknesses in websites, web-based platforms, and application programming interfaces (APIs). Testing helps uncover issues such as authentication weaknesses, access control flaws, injection vulnerabilities, and insecure data handling.
3. Mobile Application VAPT
Mobile VAPT assesses the security of Android and iOS applications. It examines potential weaknesses in application code, data storage, authentication mechanisms, communication channels, and permissions that could expose sensitive information.
4. Cloud VAPT
Cloud VAPT evaluates the security of cloud-hosted infrastructure, platforms, applications, and configurations. It helps identify risks such as excessive permissions, insecure storage, misconfigured services, and inadequate access controls.
5. Social Engineering Testing
Social Engineering Testing evaluates how effectively employees and organisational processes can withstand manipulation attempts. Controlled exercises, such as authorised phishing simulations, help identify human-related security gaps and improve security awareness.
VAPT Type
What It Assesses
Network VAPT
Internal and external network infrastructure, devices, and configurations.
Web Application and API VAPT
Websites, web applications, APIs, and their security controls.
Mobile Application VAPT
Android and iOS applications, data storage, and authentication.
Cloud VAPT
Cloud infrastructure, access permissions, configurations, and hosted services.
Social Engineering Testing
Employee awareness and susceptibility to phishing and other manipulation techniques.
Understanding Vulnerability Assessment
Definition and Purpose of Vulnerability Assessment
Vulnerability Assessment is a systematic process of identifying, analysing, and prioritising security weaknesses across an organisation's IT environment.
It examines systems, applications, networks, servers, and other digital assets to uncover vulnerabilities that could potentially be exploited by cybercriminals.
The primary purpose is to provide organisations with a clear understanding of their security risks. By identifying vulnerabilities, assigning severity levels, and recommending corrective measures, the assessment helps security teams prioritise remediation and strengthen their overall cybersecurity posture.
Techniques and Methodologies Used in Vulnerability Assessment:
A comprehensive vulnerability assessment typically involves the following activities:
Asset Discovery: Identifying and documenting critical IT assets, including networks, applications, servers, and endpoints.
Automated Vulnerability Scanning: Using specialised scanning tools to identify known vulnerabilities, outdated software, and security misconfigurations.
Application Assessment: Evaluating web applications and other software for security weaknesses.
Host Assessment: Examining servers, workstations, and other computing systems for vulnerabilities.
Network Assessment: Identifying weaknesses in wired and wireless network infrastructure, devices, and configurations.
Risk Prioritisation: Classifying vulnerabilities according to severity, potential impact, and exposure to help determine remediation priorities.
Vulnerability Assessment Tools
Vulnerability assessment tools help security professionals scan IT environments, identify known vulnerabilities, and evaluate potential security risks.
These tools analyse networks, applications, operating systems, and infrastructure components to identify issues such as outdated software, insecure configurations, missing patches, and known security flaws.
Popular vulnerability assessment tools include Nessus, Qualys, and OpenVAS. Their findings help security teams understand potential weaknesses and develop appropriate remediation plans.
Importance of Continuous Vulnerability Assessment
Cyber threats and IT environments are constantly evolving. New vulnerabilities emerge as organisations introduce applications, update infrastructure, adopt cloud services, and connect additional devices to their networks.
Continuous vulnerability assessment helps organisations maintain visibility into their changing security landscape. Regular scans and assessments enable security teams to identify emerging weaknesses, prioritise remediation, and monitor improvements in their security posture.
Rather than treating vulnerability assessment as a one-time activity, organisations should incorporate it into their ongoing vulnerability management programmes.
Understanding Penetration Testing
Definition and Purpose of Penetration Testing
Penetration Testing, commonly known as Pen Testing or Pentesting, is an authorised security testing practice that simulates real-world cyberattacks to identify and validate exploitable vulnerabilities.
During a penetration test, cybersecurity professionals use controlled techniques to assess whether weaknesses in networks, applications, systems, or security controls can be exploited.
The primary objective is to understand how an attacker could gain unauthorised access, compromise sensitive information, or disrupt business operations. The findings help organisations evaluate their actual exposure to cyber risks and strengthen their security defences.
Types of Penetration Testing
Penetration Testing is commonly classified into three types based on the level of information available to the tester.
1. Black Box Testing
In Black Box Testing, security professionals have little or no prior knowledge of the target system. The assessment simulates an external attacker's perspective and evaluates how much information and access can be obtained without internal knowledge.
2. White Box Testing
In White Box Testing, testers receive detailed information about the target environment, such as system architecture, source code, network configurations, and application details. This enables a more comprehensive assessment of potential vulnerabilities.
3. Grey Box Testing
Grey Box Testing combines elements of Black Box and White Box Testing. Testers receive limited information about the target system, allowing them to simulate an attacker who has some level of internal knowledge or access.
Penetration Testing Methodologies
An effective penetration test combines automated tools with manual testing techniques.
Automated tools help identify known vulnerabilities and potential entry points, while manual testing allows security professionals to investigate complex weaknesses, validate findings, and assess possible attack scenarios.
Depending on the scope, penetration testing may involve network testing, web application testing, API testing, mobile application testing, and cloud security testing.
The objective is to understand the potential impact of identified vulnerabilities, including unauthorised access, data exposure, privilege escalation, and service disruption.
Real-World Example: Equifax Data Breach (2017)
The 2017 Equifax data breach exposed sensitive personal information belonging to approximately 147 million people. The incident was linked to an unpatched vulnerability in the Apache Struts web application framework.
The breach highlighted the risks associated with delayed security patching and inadequate vulnerability management. It also reinforced the importance of regularly identifying, prioritising, and addressing known security weaknesses.
Proactive vulnerability assessments and appropriately scoped penetration testing can help organisations identify such security gaps and evaluate their potential impact before attackers exploit them.
VAPT Process: Step-by-Step Breakdown
A structured VAPT process helps organisations systematically identify, validate, document, and remediate security weaknesses.
While the exact approach may vary depending on the scope and testing requirements, a typical VAPT assessment involves the following four stages.
1. Initial Reconnaissance and Information Gathering
The process begins with collecting information about the target systems, applications, and network infrastructure.
Security professionals examine the authorised testing scope, identify accessible assets, understand the system architecture, and gather relevant information to plan the assessment.
This stage establishes the foundation for identifying potential entry points and security weaknesses.
2. Vulnerability Identification and Assessment
In this stage, security professionals use automated scanning tools and manual techniques to identify vulnerabilities, security misconfigurations, outdated software, and other weaknesses.
The identified vulnerabilities are analysed and assigned severity levels based on their potential impact and exploitability. This helps organisations understand which security issues require immediate attention.
3. Exploitation and Penetration Testing
During this phase, authorised testers conduct controlled attempts to exploit identified vulnerabilities.
The objective is to validate whether security weaknesses can be exploited and understand their potential impact on the organisation's systems, applications, and data.
Testing is conducted within the agreed scope and controlled conditions to avoid unnecessary disruption to business operations.
4. Reporting and Remediation
Once testing is complete, security professionals prepare a detailed VAPT report documenting the assessment findings.
The report typically includes:
Identified vulnerabilities and their severity ratings.
Affected systems, applications, or network components.
Evidence and details of validated security weaknesses.
Potential business and technical impact.
Recommended remediation and mitigation measures.
Suggested priorities for addressing identified risks.
Organisations can use these findings to implement corrective actions, strengthen security controls, and improve their overall cybersecurity posture.
VAPT Stage
Key Activities
Reconnaissance
Gather information about authorised target systems and infrastructure.
Vulnerability Assessment
Scan and analyse systems to identify security weaknesses.
Penetration Testing
Validate vulnerabilities through controlled exploitation attempts.
Reporting and Remediation
Document findings, assign priorities, and recommend corrective actions.
VAPT Tools: Popular Tools and Technologies
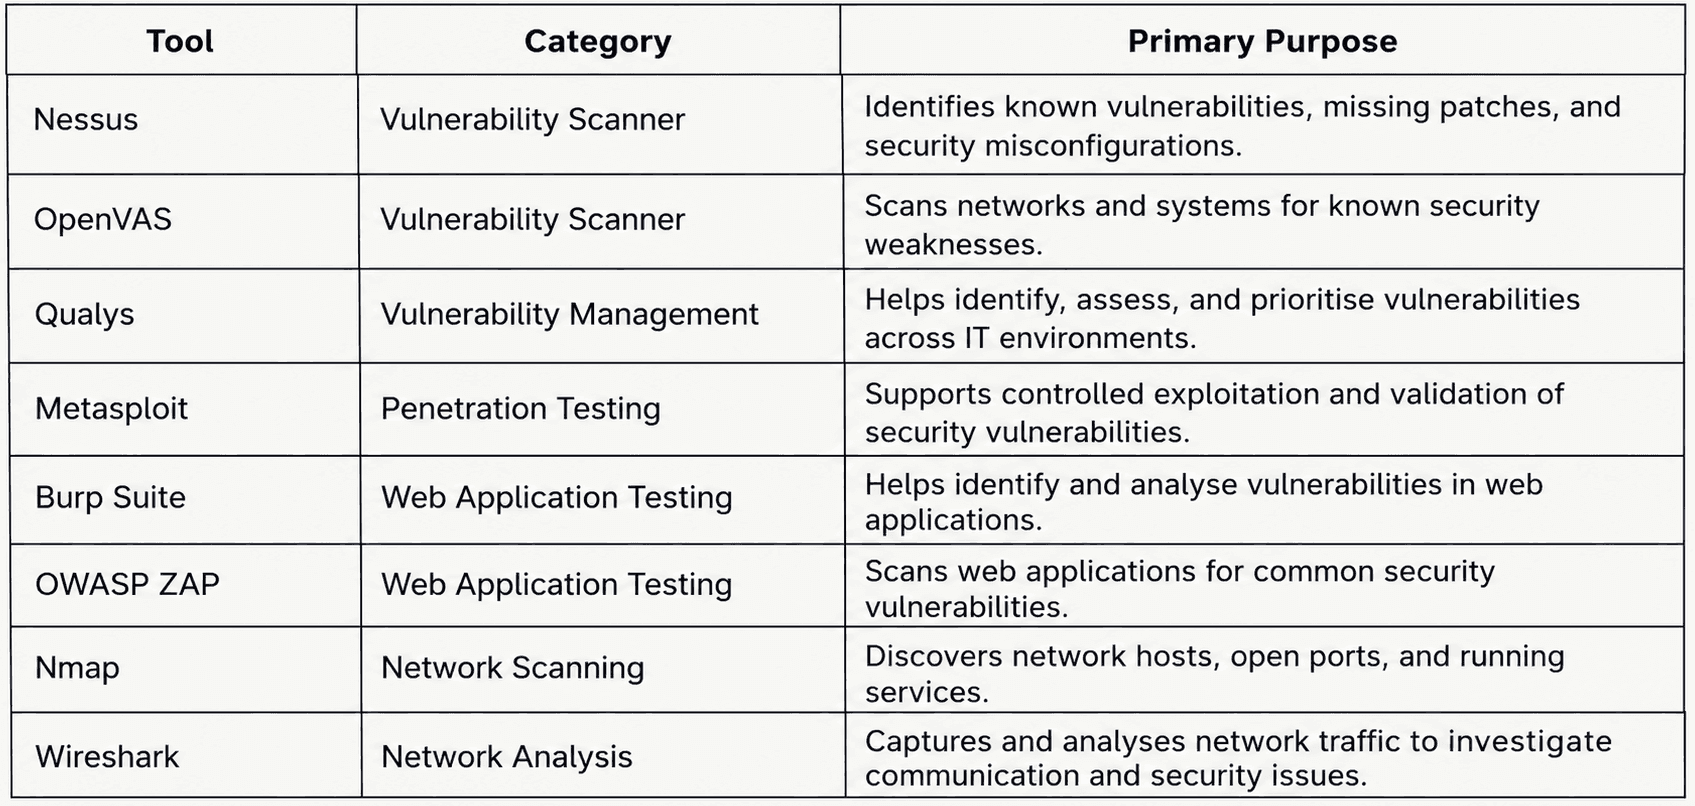
VAPT tools play an important role in identifying vulnerabilities, analysing security weaknesses, and validating potential attack paths. Security professionals use different tools depending on the testing scope, target environment, and assessment requirements.
Here are some commonly used VAPT tools:
How to Choose the Right VAPT Tools?
Selecting the right VAPT tools depends on an organisation's infrastructure, security objectives, and testing requirements.
Before choosing a tool, consider the following factors:
Testing requirements: Determine whether the assessment focuses on networks, web applications, APIs, mobile applications, or cloud infrastructure.
Automation capabilities: Evaluate whether the tool supports automated scanning and efficient vulnerability identification.
Accuracy: Consider its ability to identify relevant vulnerabilities while minimising false positives.
Scalability: Ensure the tool can support the size and complexity of the organisation's IT environment.
Reporting capabilities: Look for clear reports that help security teams understand findings and prioritise remediation.
Integration: Check whether the tool integrates with existing security platforms and vulnerability management workflows.
It is important to remember that VAPT tools support the assessment process but cannot replace the expertise of qualified security professionals. Manual analysis and validation remain essential for identifying complex vulnerabilities and understanding their potential business impact.
VAPT Services: What Do They Include?
VAPT services help organisations evaluate the security of their IT infrastructure, applications, networks, and digital assets through structured vulnerability assessments and penetration testing.
These services combine automated scanning, manual security testing, vulnerability validation, and detailed reporting to provide a comprehensive understanding of potential security risks.
Depending on an organisation's requirements, VAPT services may include:
Network Vulnerability Assessment and Penetration Testing: Identifying and validating weaknesses across internal and external network infrastructure.
Web Application VAPT: Assessing websites and web applications for security vulnerabilities.
API Security Testing: Evaluating APIs for authentication, authorisation, access control, and data exposure risks.
Mobile Application VAPT: Identifying security weaknesses in Android and iOS applications.
Cloud Security Assessment: Evaluating cloud infrastructure, configurations, permissions, and security controls.
VAPT Reporting: Providing detailed findings, risk ratings, evidence, and remediation recommendations.
Key Benefits of VAPT Services
Engaging in regular VAPT services offers several benefits:
Proactive Risk Identification: Helps organisations identify security weaknesses before attackers can exploit them.
Improved Security Posture: Provides actionable insights to strengthen existing security controls and infrastructure.
Reduced Risk of Data Breaches: Helps address vulnerabilities that could lead to unauthorised access or sensitive data exposure.
Regulatory Compliance Support: Supports security assessments and remediation efforts aligned with applicable regulatory and industry requirements.
Better Risk Management: Enables organisations to prioritise vulnerabilities based on severity, exploitability, and potential business impact.
Common Challenges in VAPT
Although VAPT is essential for strengthening cybersecurity, organisations may encounter several challenges while planning and conducting security assessments.
1. Shortage of Skilled Professionals
Finding experienced cybersecurity professionals with expertise in vulnerability assessment, penetration testing, and advanced security techniques can be challenging.
2. Complexity of Modern IT Environments
Modern IT infrastructures involve interconnected networks, cloud platforms, applications, endpoints, and third-party services. Assessing these environments requires specialised knowledge and a well-defined testing approach.
3. Time and Resource Constraints
Comprehensive VAPT assessments require adequate planning, skilled resources, and time. Limited budgets or operational constraints may affect the scope and frequency of testing.
4. Integration with Existing Security Measures
Organisations may find it challenging to integrate VAPT findings into existing security operations, vulnerability management processes, and remediation workflows.
5. Prioritising and Remediating Vulnerabilities
Large-scale assessments may identify numerous vulnerabilities. Determining which issues require immediate attention and ensuring timely remediation can be difficult without a structured risk management approach.
Choosing the Right VAPT Service Provider
Selecting the right VAPT service provider is essential for obtaining accurate security insights and actionable recommendations.
Organisations should evaluate potential providers based on their technical expertise, testing methodologies, industry experience, reporting standards, and ability to address specific security requirements.
Here are some important factors to consider:
Technical Expertise: Look for experienced cybersecurity professionals with expertise across networks, applications, cloud environments, and other relevant technologies.
Comprehensive Testing Approach: Ensure the provider combines automated vulnerability scanning with manual testing and validation.
Industry Experience: Consider experience in assessing security risks across relevant industries and technology environments.
Detailed Reporting: Choose a provider that delivers clear reports with vulnerability classifications, supporting evidence, and practical remediation recommendations.
Remediation Guidance: Ensure the provider can help security teams understand findings and prioritise corrective actions.
Customised Assessments: Select services that align with your organisation's infrastructure, business objectives, and security requirements.
Vulnerability Assessment and Penetration Testing Services by 63SATS
At 63SATS Cybertech, Vulnerability Assessment and Penetration Testing services help organisations identify security weaknesses across their IT infrastructure and strengthen their cybersecurity posture.
Through a combination of automated vulnerability scanning and expert-led manual testing, assessments evaluate potential security gaps across networks, systems, and applications.
The process helps organisations understand their exposure to cyber risks through detailed VAPT reports that document identified vulnerabilities, their severity, potential impact, and recommended remediation measures.
By combining structured security assessments with actionable insights, 63SATS helps organisations take a proactive approach to vulnerability management and build stronger cyber defences.
Explore our Vulnerability Assessment and Penetration Testing services to understand how your organisation can identify and address potential security gaps.
Best Practices for Effective VAPT
To maximise the effectiveness of VAPT, organisations should follow a structured and consistent approach to security testing.
1. Establish Regular Testing Schedules
Conduct vulnerability assessments and penetration tests at planned intervals and whenever significant changes are introduced to networks, applications, or IT infrastructure.
2. Define the Testing Scope Clearly
Identify the systems, applications, networks, and assets included in the assessment. Clearly establish testing boundaries and obtain the necessary authorisations before testing begins.
3. Combine Automated and Manual Testing
Use automated tools for efficient vulnerability discovery and manual testing to validate findings, investigate complex security weaknesses, and assess potential attack scenarios.
4. Prioritise Vulnerabilities Based on Risk
Evaluate vulnerabilities based on severity, exploitability, asset criticality, and potential business impact. Address high-risk weaknesses first.
5. Collaborate with Security Teams and Stakeholders
Ensure effective communication between cybersecurity professionals, IT teams, management, and relevant stakeholders to coordinate remediation efforts.
6. Maintain Documentation and Reporting Standards
Document assessment findings, vulnerability classifications, evidence, and remediation recommendations to support informed decision-making and future assessments.
7. Validate Remediation and Continuously Improve
After addressing identified vulnerabilities, conduct appropriate retesting to verify that corrective measures have been effective. Use assessment findings and lessons learned to improve future security testing activities.
Case Studies and Real-World Lessons
Lessons from Prominent Cybersecurity Incidents
Real-world cyber incidents demonstrate how unaddressed vulnerabilities can expose organisations to significant security and operational risks.
The Equifax data breach in 2017 is one example of how an unpatched software vulnerability can lead to the exposure of sensitive personal information.
Such incidents reinforce the importance of regular vulnerability assessments, timely patch management, and security testing to identify weaknesses before they are exploited.
How VAPT Strengthens Organisational Security and Resilience
VAPT helps organisations move beyond basic vulnerability identification by validating security weaknesses and understanding their potential impact.
Through regular VAPT assessments, organisations can:
Identify security gaps across critical IT assets.
Understand potential attack paths and exposure.
Improve vulnerability prioritisation and remediation.
Strengthen security controls and reduce cyber risks.
Support regulatory and industry security requirements.
Improve overall cybersecurity preparedness and resilience.
Conclusion
Vulnerability Assessment and Penetration Testing (VAPT) plays a critical role in helping organisations identify, evaluate, and address security weaknesses before cybercriminals can exploit them.
By combining vulnerability identification with controlled penetration testing, VAPT provides a comprehensive understanding of an organisation's security posture. It helps businesses prioritise risks, strengthen security controls, protect critical digital assets, and support regulatory compliance efforts.
As cyber threats continue to evolve, regular VAPT testing should be an integral part of an organisation's cybersecurity strategy. Investing in comprehensive VAPT services enables businesses to take a proactive approach to risk management and build a more resilient digital environment.
Frequently Asked Questions (FAQs)
1. What is VAPT?
VAPT stands for Vulnerability Assessment and Penetration Testing. It is a cybersecurity testing approach that identifies security weaknesses and evaluates whether they can be exploited through controlled attack simulations.
2. What is the difference between Vulnerability Assessment and Penetration Testing?
Vulnerability Assessment identifies, classifies, and prioritises security weaknesses, while Penetration Testing simulates controlled attacks to validate whether those weaknesses can be exploited.
3. What are the five types of VAPT?
The commonly performed types include Network VAPT, Web Application and API VAPT, Mobile Application VAPT, Cloud VAPT, and Social Engineering Testing.
4. What are the common tools used for VAPT?
Popular VAPT tools include Nessus, OpenVAS, Qualys, Metasploit, Burp Suite, OWASP ZAP, Nmap, and Wireshark. Each tool serves different vulnerability assessment, penetration testing, and network analysis requirements.
5. What is a VAPT report?
A VAPT report is a document that outlines the findings of a security assessment. It typically includes identified vulnerabilities, severity ratings, affected assets, evidence, potential impact, and recommended remediation measures.
6. What is VAPT? How Does It Work and What Is Its Step-by-Step Process?
VAPT (Vulnerability Assessment and Penetration Testing) identifies security weaknesses through vulnerability scanning and controlled attack simulations. Its process involves reconnaissance, vulnerability identification, exploitation testing, and reporting with remediation recommendations.
7. What Should Organisations Look for in VAPT Companies in India?
When selecting VAPT companies in India, organisations should evaluate technical expertise, industry experience, testing methodologies, and reporting quality. Check CERT-In empanelment if required by the applicable regulatory or contractual guidelines.
8. Why Is VAPT Important?
VAPT helps organisations identify and address security weaknesses before attackers exploit them. It reduces cyber risks, protects sensitive data, strengthens security controls, and supports regulatory compliance.
9. What Is a VAPT Certificate?
A VAPT certificate is a document issued by the security auditing provider after an assessment. However, there is no single universal VAPT certificate; the required documentation depends on regulatory, industry, or contractual requirements.