What is EDR in Cyber Security? Choosing the Right EDR Solution
Summarize this blog with :
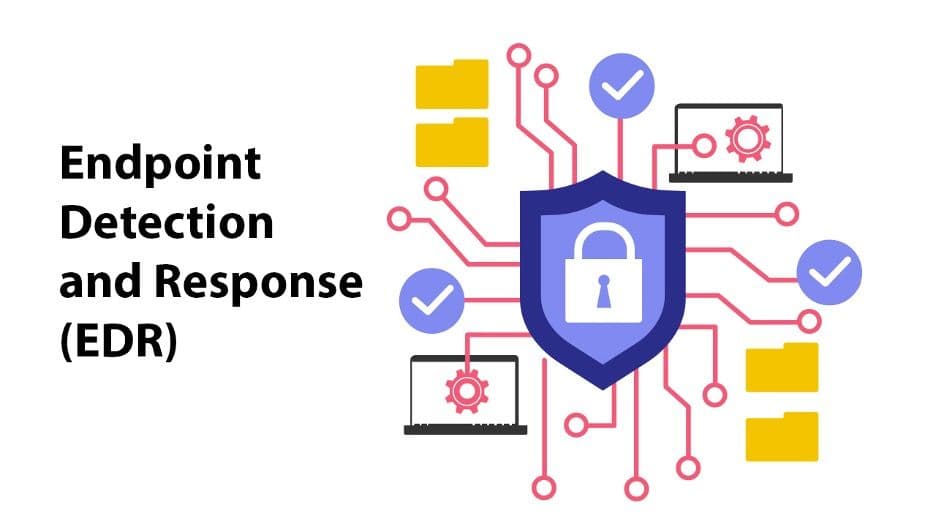
EDR security solutions can identify unusual system activity on hosts and endpoints, gather information from endpoints, and examine specific events. Then, it looks into the underlying cause of malicious behavior to notify your security team. It assists them in removing threats before malicious files have a chance to damage your environment. In an emergency, these solutions can be a true lifesaver.
Firewalls and antivirus programs are two examples of security products that we frequently use alongside endpoint detection and response solutions. Open EDR can be set up in the cloud or on-site. Since cloud-based EDR solutions offer real-time insight into all network activities, they may be more effective than on-premises solutions. So, let’s learn more about EDR in cyber security, its role in endpoint security, how to pick the right EDR solution, and more.
Understanding EDR in DepthH2
The Evolution of EDRH3
Undoubtedly, traditional endpoint security solutions are essential, but they frequently follow a reactive approach. Usually, they involve firewalls and antivirus software meant to stop known dangers from getting into our vital systems, which house our most valuable possessions, which are the data kept on these networks and systems.
However, these solutions might not hold up in the face of increasingly complex and dynamic dangers. Here, EDR in cybersecurity shows itself to be the most effective tool in the fight against these vicious and dangerous dangers. EDR emphasizes detection and reaction more than typical security methods, which mostly concentrate on prevention.
Key Components of EDRH3
Endpoint DetectionH4
This speaks to the capability of EDR to be installed on an endpoint, capture endpoint data, and then store that data elsewhere for later analysis. EDR can be installed independently or as a complete endpoint security solution component.
Incident ResponseH4
The term "incident response" describes EDR's capacity to take pictures of an endpoint at different points in time and, in the case of an attack, re-image or roll back to a previous stable state. Administrators can also isolate endpoints with EDR to stop them from spreading further throughout the network.
Threat HuntingH4
EDR searches for files, processes, and applications that match known malware specifications. Another feature of threat hunting is the capacity to go through all open network connections for possible illegal access.
Role of EDR in Endpoint SecurityH2
A company's endpoint security policy has long been crucial to its cybersecurity plan. While network-based defenses successfully block many cyberattacks, some will still get through, and some (such as malware carried by portable media) can completely circumvent these defenses.
Your business can deploy defense in depth and improve its chances of seeing and countering these threats by utilizing EDR solutions.
How EDR Differs from Traditional Antivirus SolutionsH2
Traditional firewall and antivirus software are enhanced with more powerful security features by an EDR system. Antivirus software lacks many features and benefits these tools and solutions offer.
While monitoring endpoint behaviors and operations, they also act against malware. Conversely, an antivirus program does nothing more than find and eliminate viruses. It is unaware of the virus's activities. The antivirus is not as comprehensive as contemporary EDR solutions. Their scope is limited to detecting, eradicating, and scanning malware and viruses.
That isn't to say that a business should give up on antivirus software. To achieve optimal network security, use antivirus software and EDR tools together.
Key EDR Functions in Cyber SecurityH2
Correlation Engine: It examines the information gathered and spots questionable behavior.
Data Collection: This agent searches the network for data from different sources.
Administrator Console: It makes system management and incident investigation possible for security staff.
Reaction/Response Module: It takes action (such as quarantining a file or blocking an IP address) in response to the correlation engine's output.
Benefits of Implementing EDR in CyberSecurity H2
Improved Incident ResponseH3
Analysts may need to spend six to seven hours looking into each alert if there isn't enough background information and context. Additionally, based on the quantity of endpoints, they could get hundreds of notifications in a single day.
Enhanced Visibility into Endpoint ActivitiesH3
They enable security teams to swiftly recognize and address risks by giving them real-time visibility into endpoint activities.
Proactive Threat IntelligenceH3
Threat intelligence gives EDR the much-needed context by giving more in-depth information about active attacks and specifics about the adversary.
Choosing the Right EDR Solution - What should you Look for in an EDR solution? H2
Factors to ConsiderH3
You may feel secure knowing your company is secure when you partner with a provider who provides a complete solution. So, here’s how to find one of the best EDR solutions.
ScalabilityH4
It's important to find out the possibilities for adding new parts and features to your EDR system from your vendor. Additionally, you want to think about how the system will manage any spike in traffic, particularly if it expands in the future and the number of remote devices increases.
Integration CapabilitiesH4
It is crucial to confirm that the EDR in cybersecurity you are considering is compatible with the security solutions you currently have. Your IT/security team's workload will be lighter and more efficient as a result. However, for EDR technologies to function well, they must be able to integrate with other security systems that monitor, plan, and carry out counterattack measures.
User-Friendly InterfaceH4
EDR tools need to be simple to use and put into practice. They must provide an easy-to-use interface and unambiguous alarms that security teams can respond to. EDR administrators should be able to examine each endpoint's security state, set up policies, and look into and handle security problems using the tools' centralized management consoles.
Customization OptionsH4
Developing your threat detection model or fine-tuning the pre-existing one may be desirable, depending on your experience with staff. Presets are tailored for optimal performance, according to EDR providers. Nevertheless, no two firms are alike, and no default machine-learning technique is ideal in every circumstance.
Vendor Reputation and SupportH4
Ensure you know the assistance options accessible to you and the account manager's degree of competence beforehand. Although keep in mind any incentives present on their end of the transaction, managed service providers are frequently in a strong position to assess the relative degrees of support offered by various suppliers if you use them.
Common Pitfalls to Avoid When Selecting EDR SolutionsH3
Believing that EDR in cybersecurity is a "set it and not worry about it" kind of solution is one of the biggest mistakes. It isn't realistic to think that you can simply install the software and have it take care of everything for you. A significant number of internal talent must be able to understand and use the program.
Not having knowledgeable operators to use the software is another mistake. Due to its ability to identify problematic but not always dangerous objects, EDR software needs operators to be relatively skilled. Furthermore, some EDR technologies can not be very scalable, which makes it challenging for businesses to strengthen their security posture.
Also, restricted scalability can lead to delays or outages during periods of high demand, impairing an organization's capacity to identify and address security concerns promptly.
Why is EDR important in Cyber Security? H2
Cyber threats are always changing. Attackers now use extremely advanced technologies to get around traditional security procedures. Therefore, it's imperative to implement a system that automatically defends end users, IT assets, and endpoint devices from ransomware and malware businesses.
EDR in cybersecurity accomplishes this same thing. It leverages data analytics techniques while monitoring and storing endpoint-system-level behaviors. This enables it to identify suspicious system behavior, stop potentially dangerous behaviors, and provide useful recommendations for fixing issues.
Comparing Top EDR SolutionsH2
Reviewing Leading EDR Products in the MarketH3
63 SATSH4
Detection Capabilities: The EDR team at 63 SATS are highly skilled cybersecurity personnel with expertise in detecting, assessing, and eliminating endpoint threats.
Incident Response Functionality: This EDR platform can seamlessly conduct major incident response activities after considering predefined rules to remediate them instantly and simply things for security analysts.
User Interface and Experience: This tool’s easy-to-use interface and navigation impresses many companies. Although relatively new, 63 SATS ranks above average regarding support and ease of deployment.
Performance Metrics: According to users, 63 SATS is excellent in terms of both response times and detection rates. They ensure fast response, advanced detection, and quick remediation.
Cost Analyses: Although this platform offers price quotes for EDR services upon request and your business needs, existing users do find it more reasonable than other platforms.
Implementing EDR in Your BusinessH2
Put EDR into practice to strengthen your company's cybersecurity stance. Establishing industry-specific policies, integrating EDR in cybersecurity with pre-existing security systems, and creating detection and response methods are recommended. Give your employees thorough instructions on recognizing threats and taking appropriate action.
Optimize alert setups and leverage threat intelligence feeds to prepare for potential problems such as false positives and data overload. Although implementing EDR necessitates advance planning, the improved visibility and quicker incident response will greatly improve your security stance.
Future Trends in EDR Technology H2
With more SMBs adopting endpoint detection and response, autonomous response capabilities emerging, privacy and data protection being prioritized, and threat hunting evolving, the future of endpoint detection and response appears bright. These developments will change the cybersecurity scene in 2024, giving companies stronger and more efficient defenses against online attacks.
There will soon be new trends that enhance EDR in cybersecurity.
Enhanced compatibility with other security tools.
AI will raise the bar for EDR solutions significantly.
Increased Attention to Insider Threats.
Enhancement of Response and Endpoint Detection Technologies.
Conclusion H2
Finally, endpoint detection and response technology is an essential part of any security plan. Security teams can swiftly discover and address threats because of its powerful threat detection, real-time visibility, and incident response capabilities.
EDR in cybersecurity is a crucial security component that needs to be safeguarded in today's digital environment since it can assist firms in adhering to several laws and requirements.
So, now that you are aware of the crucial function EDR tools play in a strong cybersecurity environment, your attention must be directed toward selecting the appropriate EDR product and deployment plan. Get the best cybersecurity software, 63 SATS, and level up your endpoint detection and security.
FAQs H2
How Does EDR Enhanced Endpoint Security?
EDR security solutions report to one centralized platform and continuously gather and analyze data. This allows a security team to monitor every endpoint on the network from a single console, giving them complete visibility.
Can EDR Prevent Cyber Attacks?
An EDR tool keeps track of all activity data on a consolidated dashboard and performs continuous endpoint monitoring to prevent cyber attacks.
Are EDR Solutions Suitable for Small Businesses?
EDR enables small firms to establish an enterprise-grade strategy by multiplying the tools they now have and leveraging their present expertise, budget, and solutions.
Can EDR Solutions Integrate with Existing Security Infrastructure?
Regarding centralized monitoring and response, EDR in cybersecurity can frequently be integrated with pre-existing security infrastructure, such as SIEM systems.
How Often Should EDR Solutions Be Updated?
It depends on the latest trends and updates in cybersecurity and other factors like your company’s cybersecurity needs and budget.
Experience Our Solutions in Action
Explore interactive demos and see how 63SATS helps you stay ahead of evolving cyber threats.